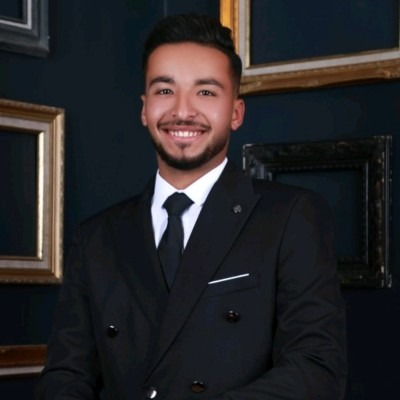
> KHALED HANI
Cybersecurity Graduate • Penetration Testing • Red Teaming • Offensive Security
Cybersecurity graduate focused on Offensive Security, Penetration Testing, Web Application Security, and Red Teaming. Hands-on skills developed through intensive self-driven security training, comprehensive Ethical Hacking and OSCP tracks, deep Network+ fundamentals, Red Teaming tactics, Udemy courses, and continuous real-world labs on TryHackMe and Hack The Box. Experienced with Kali Linux, Nmap, Burp Suite, Metasploit, Wireshark, SQLMap, and offensive assessment methodologies. Seeking an entry-level opportunity in Penetration Testing and Offensive Security where I can apply my practical knowledge and continue advancing toward a professional Red Team role.
Nmap, Burp Suite, Metasploit, Wireshark, SQLMap, Gobuster, Hydra, Hashcat, John the Ripper, Nikto, OpenVAS, OWASP ZAP.
Kali Linux, Windows, Parrot, BlackArch • Python, JS, Bash, SQL, Git, Docker, Google Colab.
Web Application Security, Network Penetration Testing, Vulnerability Assessment, Information Gathering, OSINT.
TCP/IP, DNS, HTTP/HTTPS, FTP, SSH, Network Troubleshooting • OWASP Top 10, MITRE ATT&CK, CVSS.
Irbid National University, Irbid, Jordan
Graduated: 2026 • Irbid, Jordan
Self-Driven Security Labs & Intensive Training • Amman, Jordan
Undertook intensive, self-directed offensive security training covering Ethical Hacking, OSCP curriculum, CompTIA Network+ protocols, and Red Teaming operations. Completed numerous hands-on machine exploitations, boot2root challenges, and network pivot labs across TryHackMe and Hack The Box, along with specialized offensive courses on Udemy.
Linux Administration, Windows Administration, Network+, Ethical Hacking, Penetration Testing, Bug Bounty, Python for Cybersecurity. Hands-on labs and Capture The Flag (CTF) challenges on TryHackMe and Hack The Box.
• Arabic: Native
• English: Professional Working Proficiency